palaniappan p9 min
AWS CloudTrail Production Setup: Multi-Region Trails, Log File Validation, and CloudTrail Lake
Production CloudTrail: multi-region org trails, log validation, CMK, Lake + Athena. July 2026 checklist — Event History is not enough.
FactualMinds Blog
Expert perspectives on AWS cloud consulting, generative AI, and enterprise solutions.
Production CloudTrail: multi-region org trails, log validation, CMK, Lake + Athena. July 2026 checklist — Event History is not enough.
EBS default encryption per Region, CMK lifecycle, block public snapshots. July 2026 baseline checklist — retrofit is expensive.
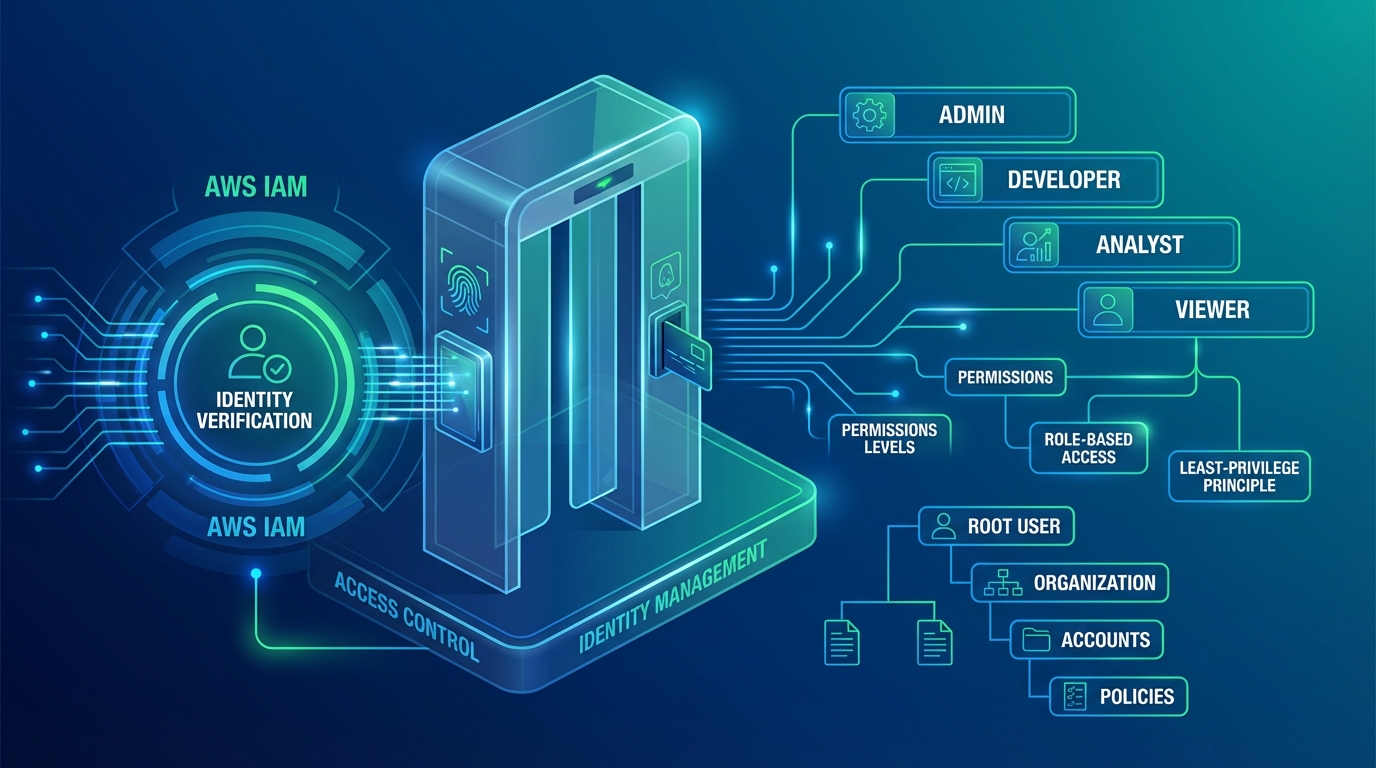
AWS IAM Identity Center is the AWS-native workforce SSO and identity-propagation service. This guide covers federation from Okta / Microsoft Entra ID, permission-set design, attribute-based access control (ABAC), identity propagation to Q Business / Redshift / QuickSight / S3 Access Grants, and the migration off long-lived IAM users.
AWS KMS ML-KEM hybrid TLS + ML-DSA signatures. July 2026: when to enable PQC, performance, migration checklist for HNDL risk.
Macie + Detective: S3 DSPM and forensic graphs. July 2026 — scope costs, KMS decrypt, paired Security Hub pipeline.
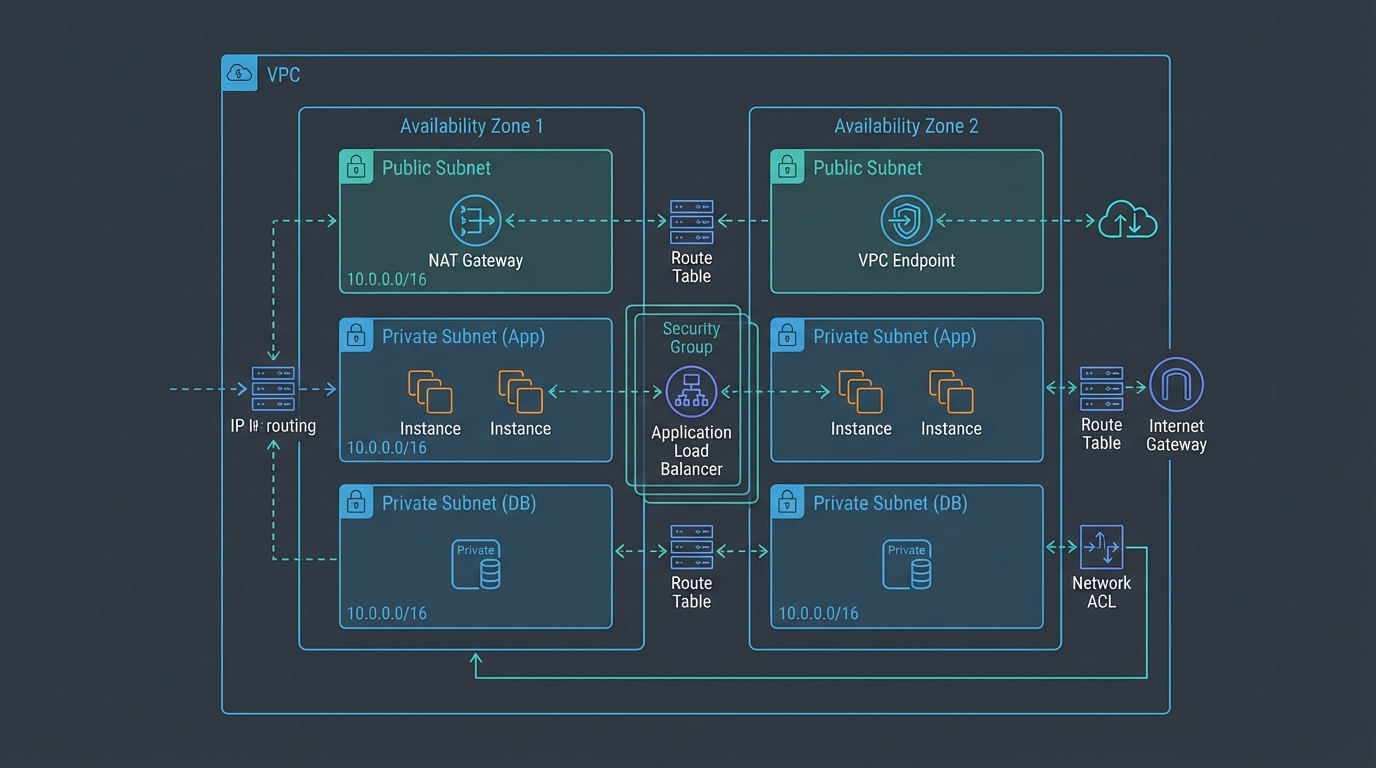
Network Firewall + Firewall Manager for Org-wide L3–L7. July 2026: centralized inspection, Suricata, TLS bypass, rollout checklist.
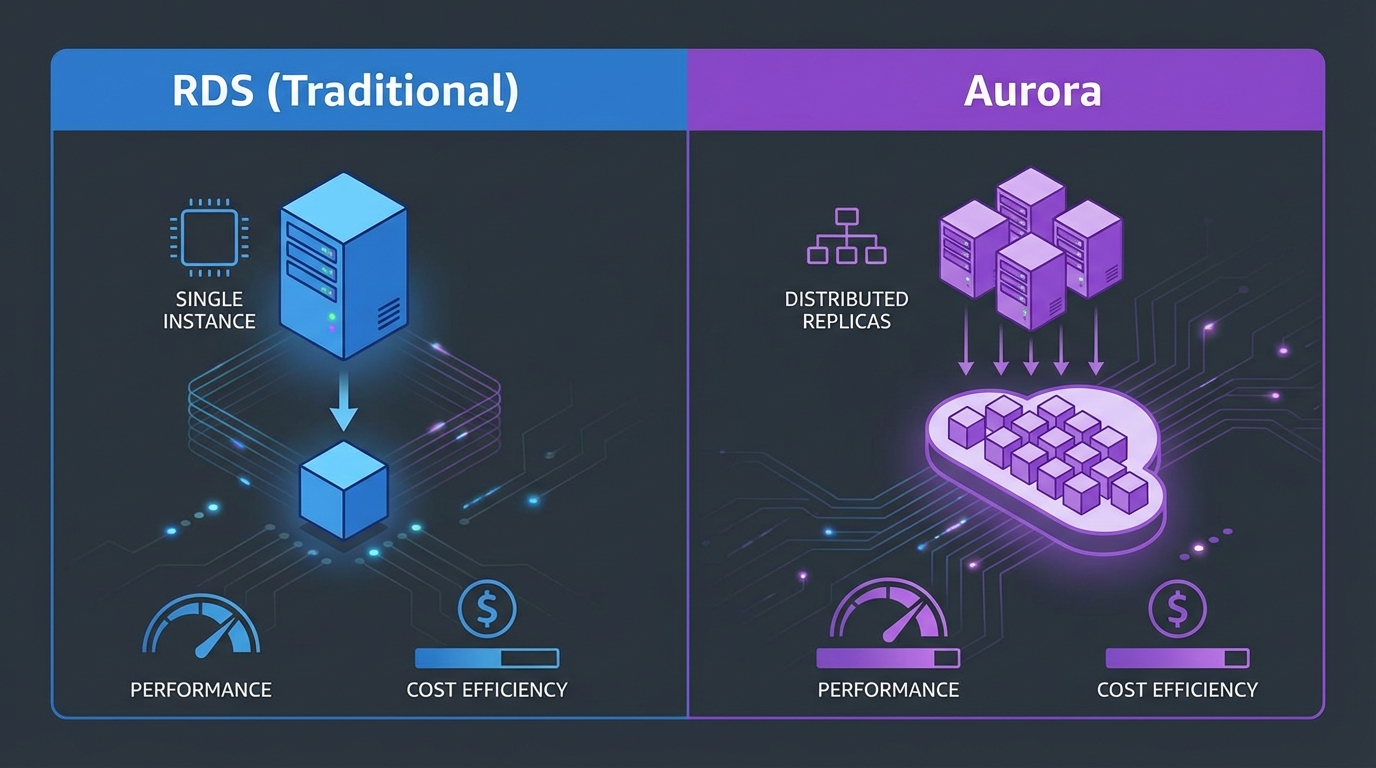
RDS performance: gp3 IOPS, Performance Insights / Database Insights, Proxy, replicas, ElastiCache. July 2026 tuning checklist.
Hardening quick wins: private DMS, OpenSearch encryption, SageMaker VPC-only, Lambda runtime EOL. July 2026 checklist.
Verified Access ZTNA: Cedar policies, Identity Center, TCP endpoints (GA). July 2026 Client VPN migration checklist.
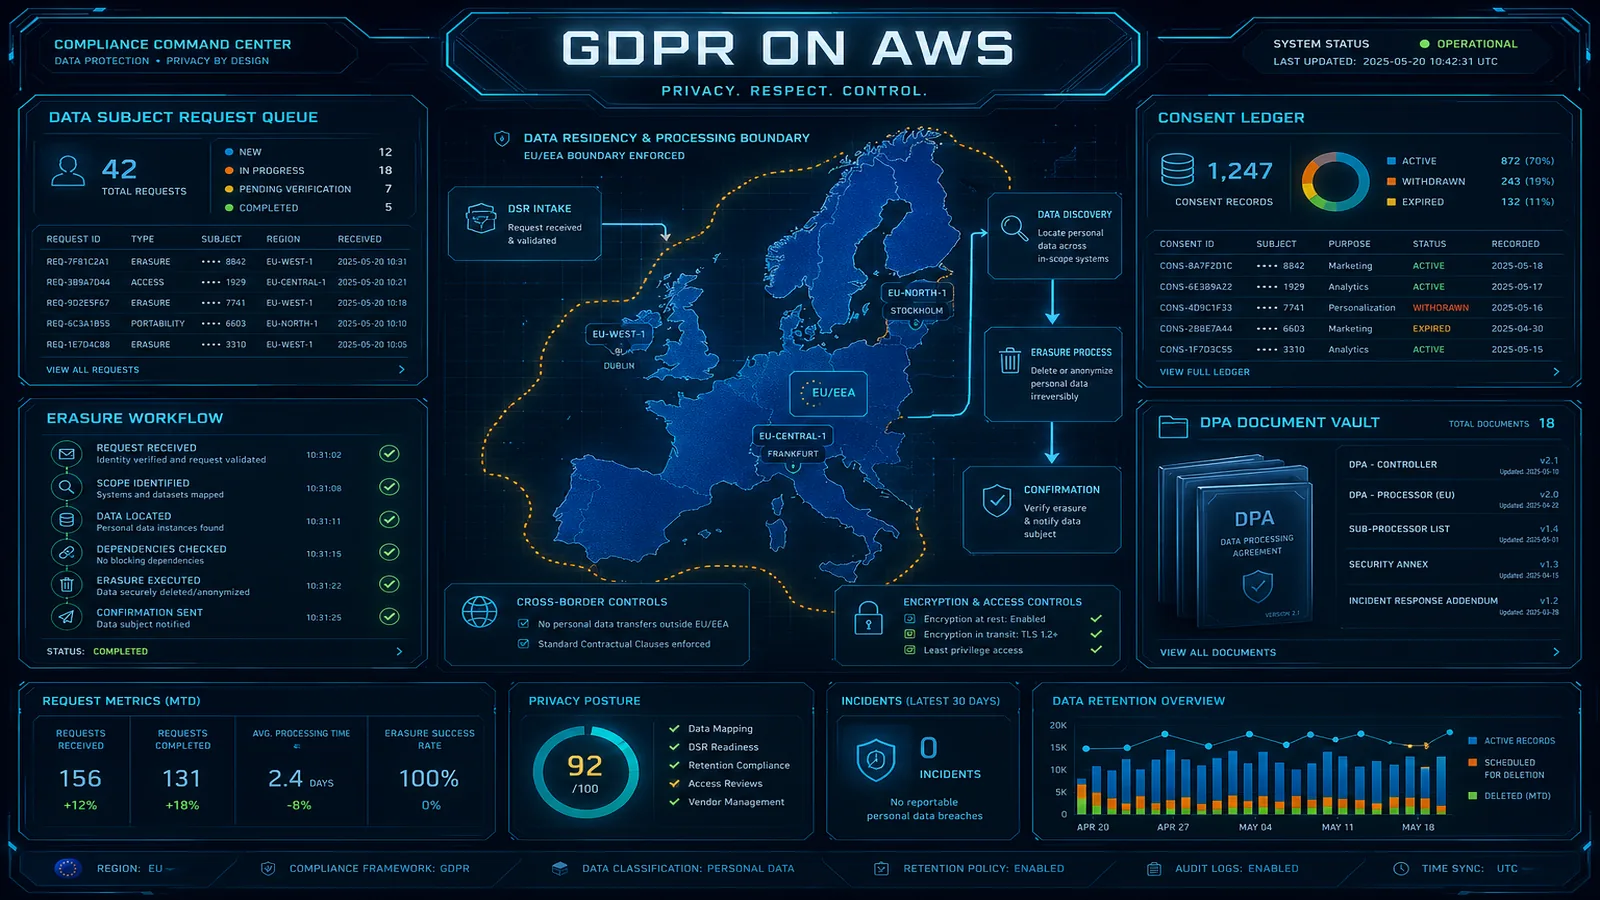
DORA on AWS since Jan 2025: RoI, TLPT/TIBER-EU, incident clocks, Artifact addendum. July 2026 readiness checklist.
EU AI Act compliance on AWS — risk classification, prohibited practices, GPAI obligations, the high-risk Annex III framework (enforceable 2 August 2026), and the AWS-native control mapping using Bedrock Guardrails, SageMaker Model Cards, and Audit Manager governance.
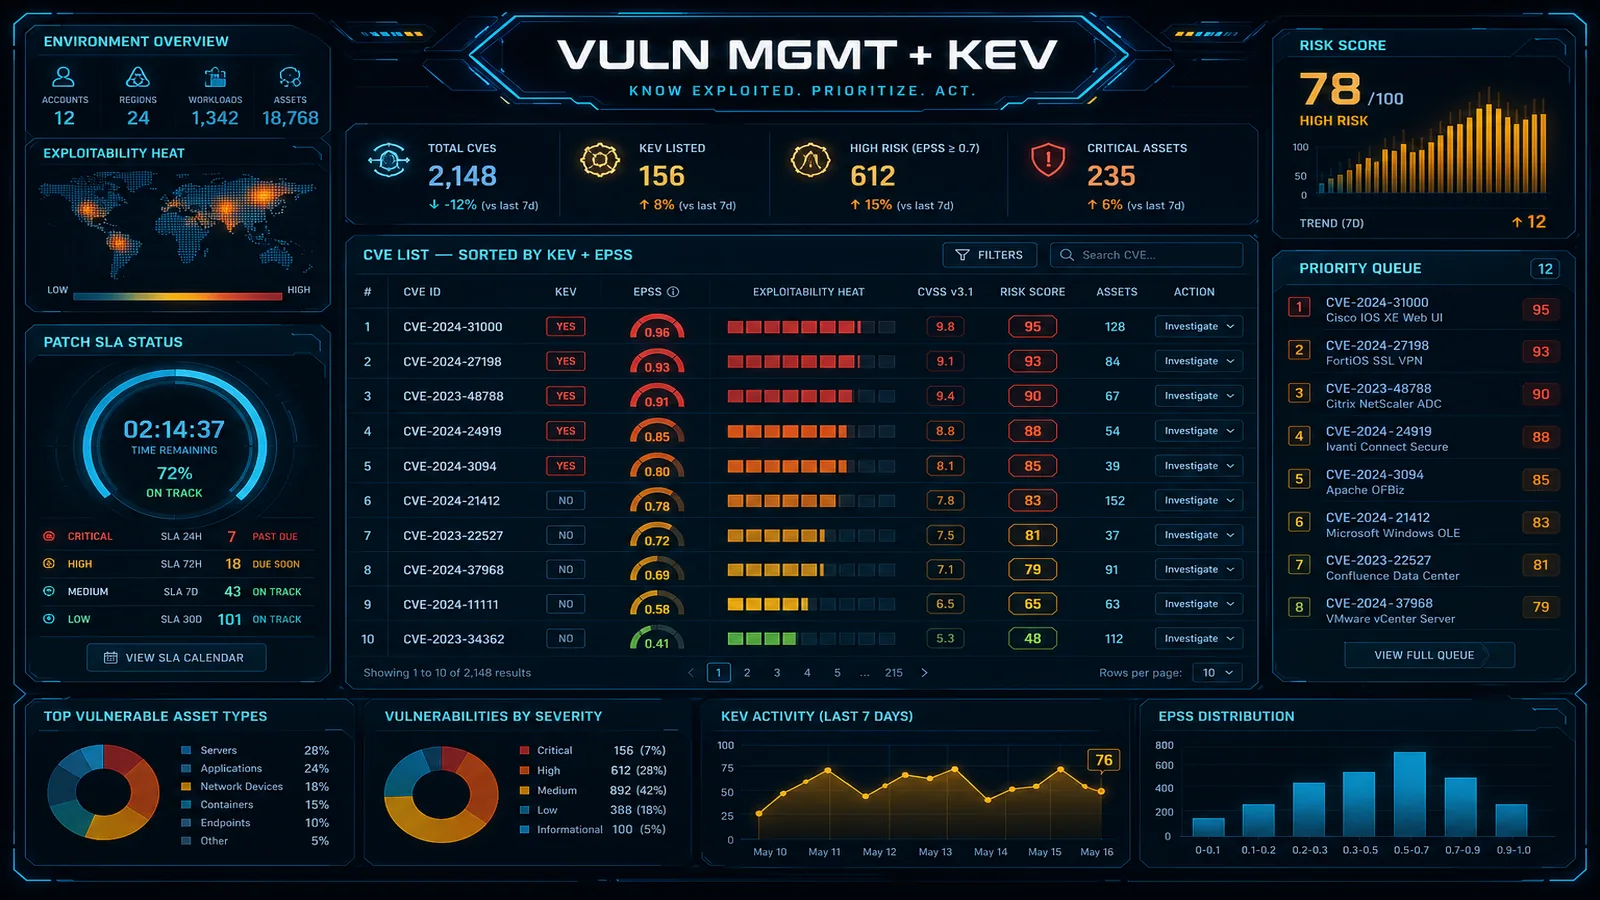
How to build a vulnerability management program that scales beyond CVE-counting. Inspector v2 deployment, CVSS + CISA KEV + reachability for risk-based prioritization, container and IaC scanning in CI/CD, and remediation SLAs that survive audits.